publications
Please refer to my Google Scholar for a complete publication list.
2026
- KBS
 DualVeil: Persistent and invisible backdoor attacks in federated learning via dual optimizationMaozhen Zhang, Mengnan Zhao, Wei Wang, and 1 more authorKnowledge-Based Systems, 2026CAS 分区: 中科院1区top新锐分区: 新锐1区top
Federated learning is gaining attention owing to its capability to protect data privacy in distributed environments. However, its decentralized architecture makes it susceptible to backdoor attacks. Although various backdoor injection methods have been proposed, achieving trigger stealthiness and backdoor attack persistence remains challenging. We address such issues by proposing DualVeil, a novel attack framework that jointly optimizes persistent parameter maximization optimization and triggers invisibility minimization optimization. Specifically, persistent parameter maximization optimization enhances attack persistence using historical gradients and stable parameters to develop constrained updates within the parameter hypersphere. Meanwhile, the trigger invisibility minimization optimization module refines the trigger mechanism via feedback-guided optimization, thereby reducing its perturbation. Extensive experiments demonstrate that DualVeil can effectively inject a covert backdoor mapping into the global model without compromising its main-task performance. Comparative studies of the state-of-the-art backdoor attacks across five aggregation schemes further validate the superior attack efficacy of DualVeil. Our code is available at https://github.com/Maozhen-Zhang/DualVeil.git.
- IoT-J
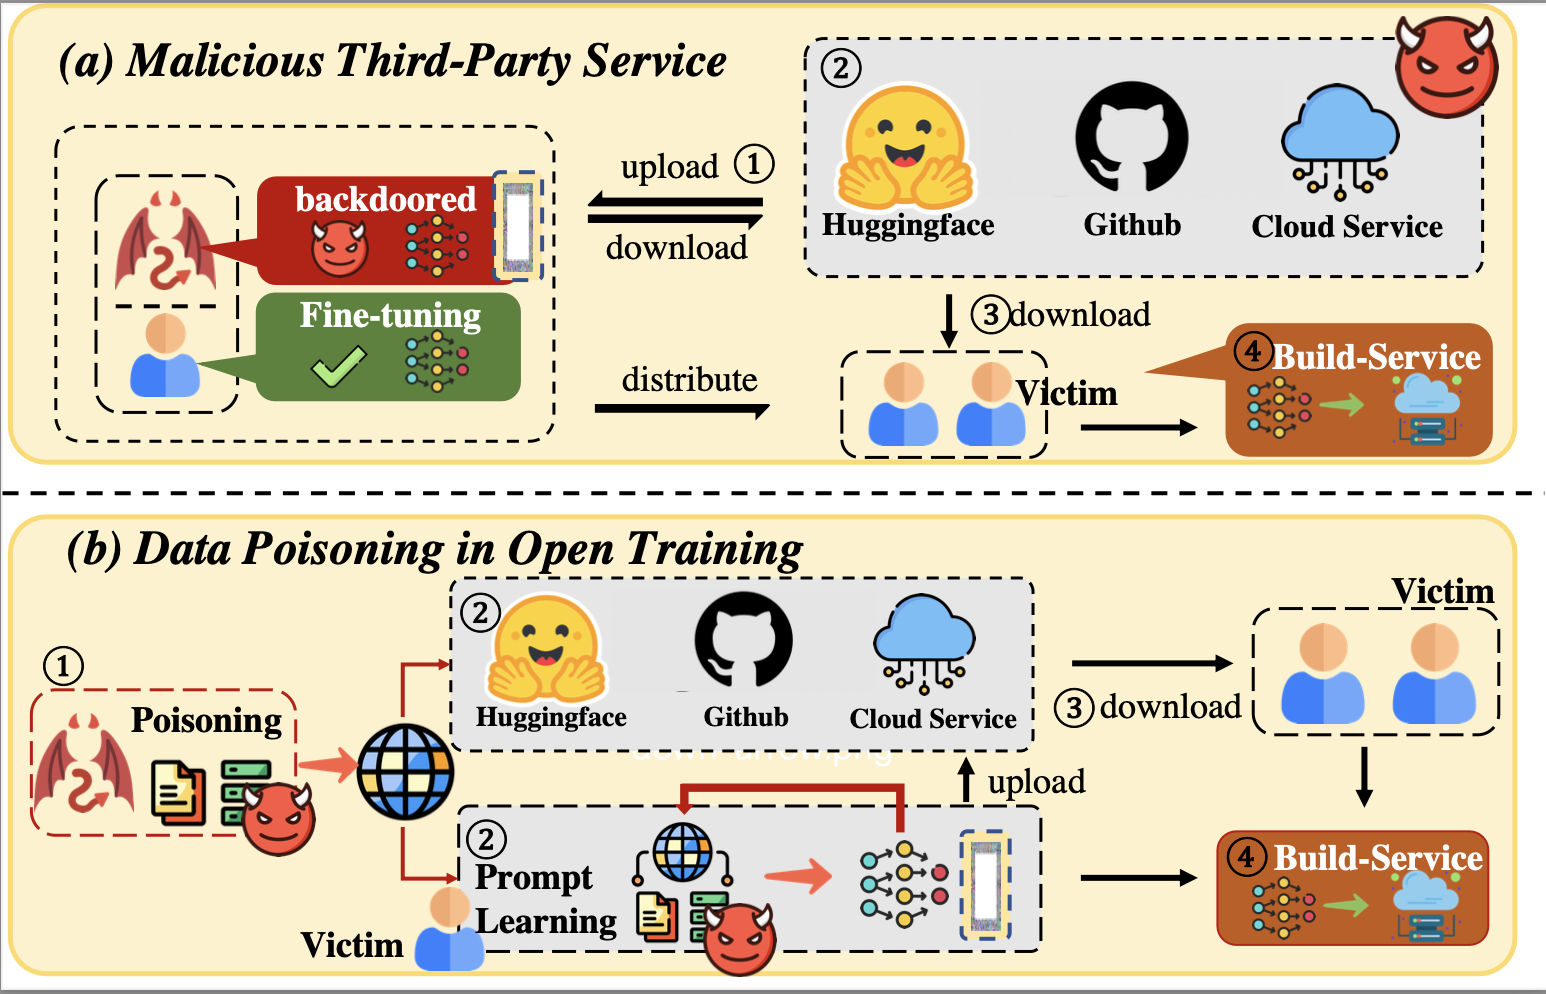 Stealthy Backdoor Carriers: The Threat of Visual Prompts to CLIPMaozhen Zhang, Mengnan Zhao, Wei Wang, and 1 more authorIEEE Internet of Things Journal, 2026CAS 分区: 中科院二区top新锐分区: 新锐1区top
Visual Prompt (VP) learning has rapidly emerged as a popular paradigm for parameter-efficient task adaptation in CLIP-based models. However, while VP optimizes pixel-space vectors without altering CLIP’s internal weights, this decoupled design inadvertently introduces critical security vulnerabilities. Attackers can exploit VP to implant covert backdoors using imperceptible trigger patterns that bypass traditional anomaly detection mechanisms, posing significant risks to real-world applications. Existing backdoor techniques, however, rely on visually noticeable patterns and exhibit inconsistencies in representation alignment, which make them prone to detection and ineffective against robust defenses. In response to these limitations, we propose Stealthy Backdoor Carriers (SBC), a novel attack framework that leverages CLIP’s inherent vulnerabilities to covertly and persistently inject backdoors. SBC adopts a dual-constrained optimization strategy that balances imperceptibility—minimizing trigger perturbations for visual stealth—and cross-modal embedding alignment—ensuring poisoned and target samples share consistent representations within CLIP’s multimodal space. Experimental results across five benchmark datasets demonstrate SBC’s exceptional effectiveness, achieving a +49.63% improvement in attack success rate relative to existing methods while maintaining robustness against advanced defenses like Neural Cleanse. Our work highlights the need for reevaluating the security implications of VP learning frameworks and provides valuable insights for mitigating prompt-based vulnerabilities in AI systems. Our code is available at https://github.com/Maozhen-Zhang/sbc.git.
- JISA
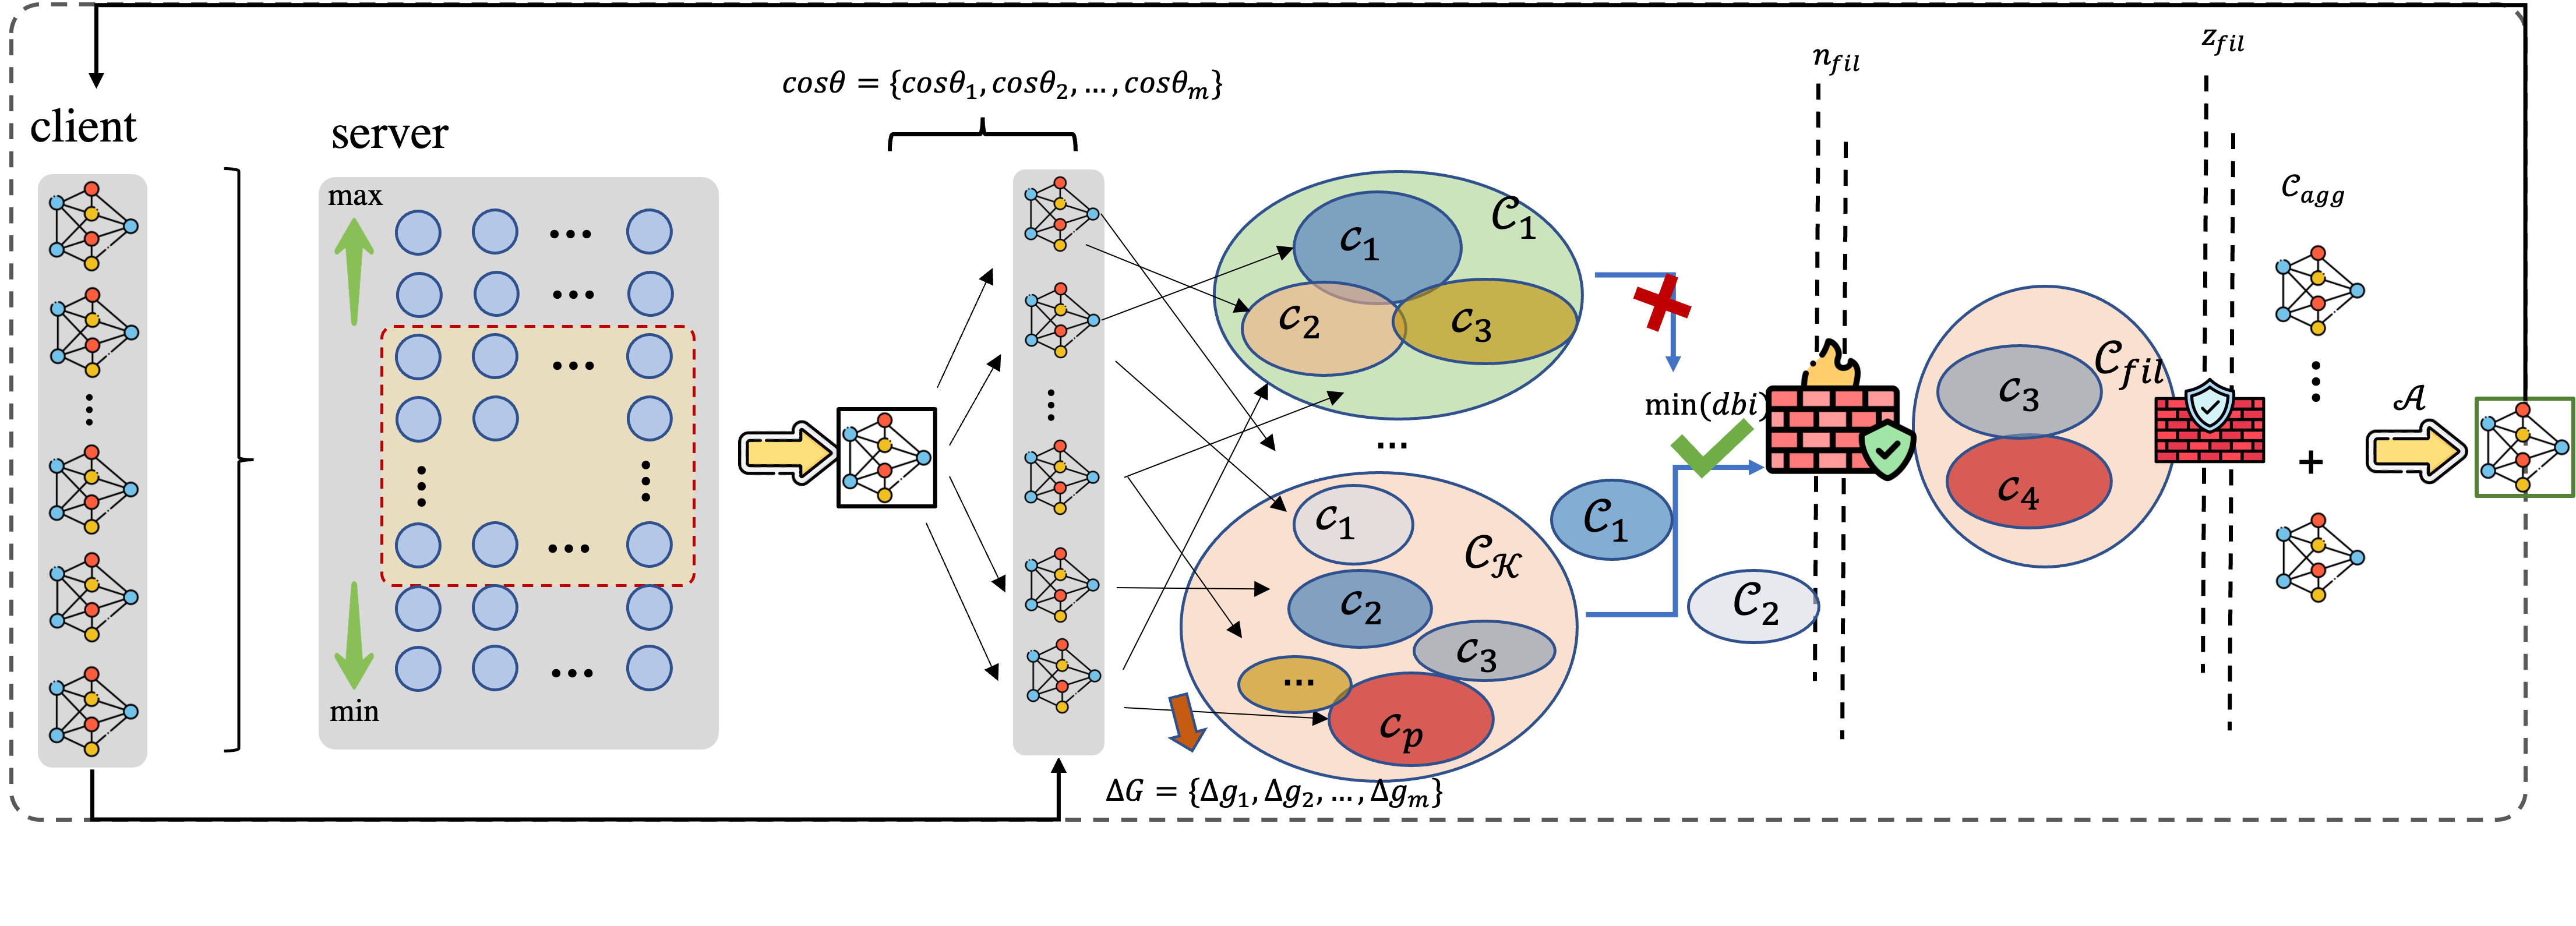 AMF-CFL: Anomaly model filtering based on clustering in federated learningBo Wang, Xiaorui Dai, Wei Wang, and 3 more authorsJournal of Information Security and Applications, 2026新锐分区: 新锐二区
Federated learning (FL) allows multiple participants to collaboratively train a shared model without exposing their local data, thereby mitigating the risk of data leakage. Despite its advantages, FL is vulnerable to attacks by malicious clients, and existing defense mechanisms, while effective under independent and identically distributed (i.i.d.) settings, often exhibit degraded performance in non-i.i.d. scenarios where client data distributions differ. To overcome this limitation, we propose AMF-CFL, a robust aggregation algorithm specifically designed for federated learning under non-i.i.d. conditions. AMF-CFL reduces the influence of malicious updates through a two-step filtering strategy: it first applies multi-k-means clustering to identify anomalous update patterns, followed by z-score-based statistical analysis to refine the selection of benign updates. Comprehensive evaluations against four untargeted and two targeted attack types demonstrate that AMF-CFL effectively preserves the integrity and robustness of the global model, offering a reliable defense in challenging federated learning environments.


2025
- JISA
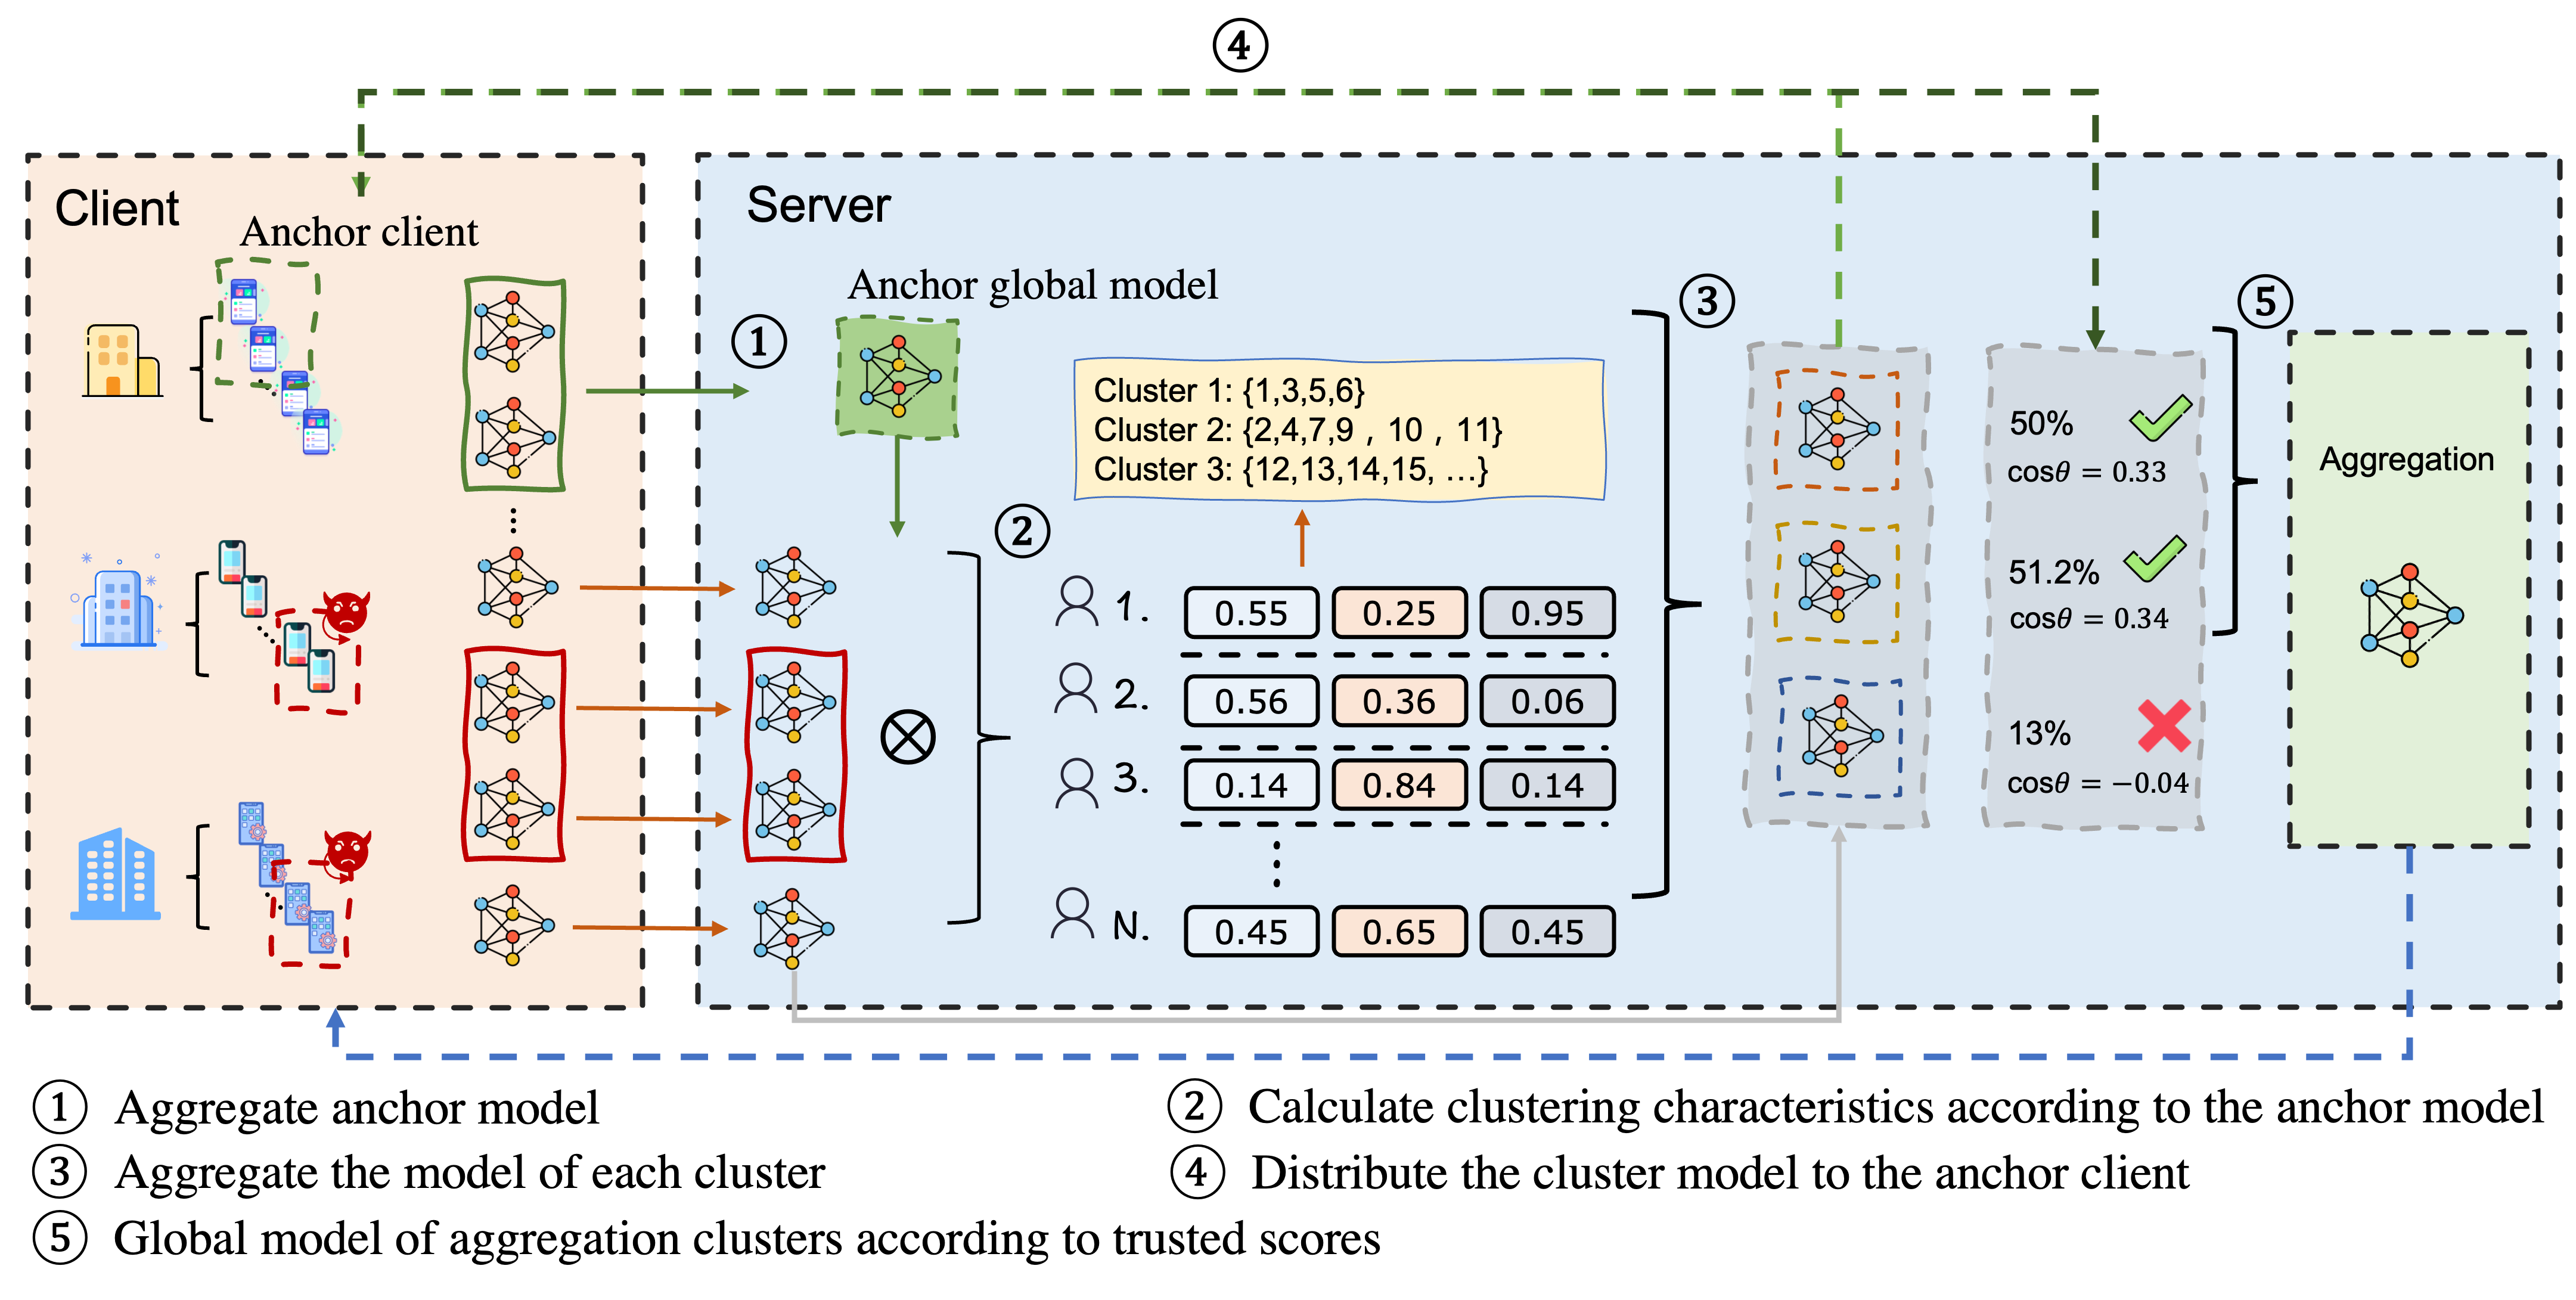 Robust clustering federated learning with trusted anchor clientsMaozhen Zhang, Yi Li, Fei Wei, and 2 more authorsJournal of Information Security and Applications, 2025新锐分区: 新锐二区
Federated Learning (FL) is a distributed machine learning framework that has attracted widespread attention. However, its decentralized architecture makes it vulnerable to attack with malicious data or model injection. While existing methods are can defend against a limited number of malicious clients, the challenge of defending against model poisoning attacks from a large number of malicious clients remains an unresolved issue. To address these challenges. We propose the Robust Clustering Federated Learning with Trusted Anchor Clients, which aims to provide clean global models for specified trusted client’s enterprise (trusted client as anchor client), even in the presence of a substantial number of malicious clients. Specifically, it performs classification by extracting clustering factors from the differences between anchor clients and other clients. It then identifies trustworthy clusters as aggregation clusters to identify the most likely benign clients. Extensive experiments on two datasets demonstrate that our method maintains robust defense efficacy, even in scenarios involving numerous malicious clients (more than 50%) or highly non-independent, non-identically distributed data.

2021
- Inf. Sci.
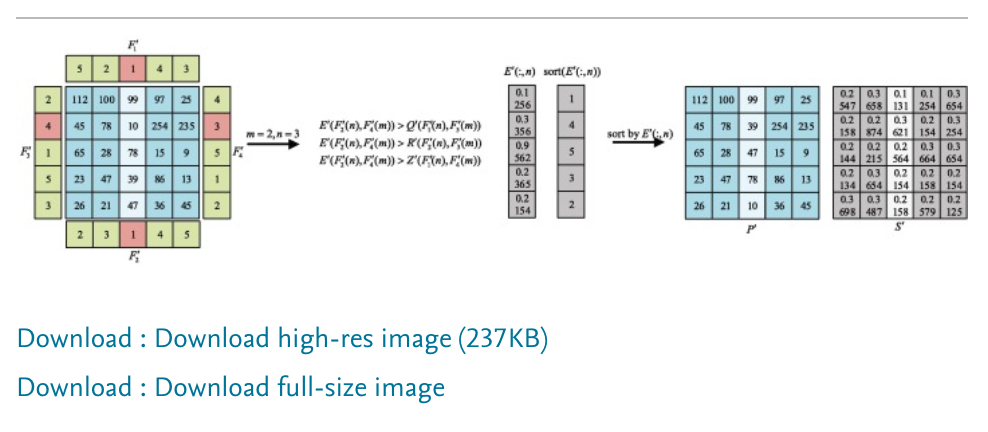 An image encryption algorithm based on new chaos and diffusion values of a truth tableXingyuan Wang, and Maozhen ZhangInformation Sciences, 2021新锐分区: 新锐1区top
This paper proposes a new chaotic system based on two parameters. The proposed chaotic system has good chaotic characteristics, and it can be shown that the chaotic system is suitable for image encryption through a variety of simulation experiments. Based on this system, we propose a new image encryption algorithm. The algorithm uses nonlinear chaotic sequences for row, column, and diagonal scrambling and diffusion in two directions. When scrambling, the diffusion matrix generated by the chaotic system is dynamically upset, and the image scrambling direction is determined by the relative coordinates of multiple chaotic systems. When diffusing, two matrices are used to change the pixel value: one is the matrix processed by scrambling, and the other is the matrix generated by the truth table. The resulting encrypted image is affected by both the chaotic system and the truth table rules. Theoretical analysis and experimental results show that the image encrypted by this algorithm has high security.
- A new image encryption algorithm based on ladder transformation and DNA codingXingyuan Wang, and Maozhen ZhangMultimedia Tools and Applications, 2021
In this paper, a new scrambling algorithm is proposed to reduce the correlation between the image pixels in three directions. In this paper, this algorithm is called ladder scrambling, and the image is scrambled multiple times in the form of diagonal lines. In terms of diffusion, DNA coding is used, and the secondary processing of the image is performed through DNA coding to change the pixel value of the image. The final encrypted image is affected by three conditions: the number of scrambling algorithms, the selection of DNA coding rules, and the key of the chaotic system. Theoretical analysis and experimental results show that the algorithm is safe and effective.
- High-sensitivity synchronous image encryption based on improved one-dimensional compound sine mapXingyuan Wang, and Maozhen ZhangIET Image Processing, 2021
An improved one-dimensional compound sine map is introduced. The evaluation of this chaotic system shows that it has high sensitivity and random chaotic behaviour. Based on this chaotic system, a new fast image encryption scheme is proposed. Through the cross-processing of multiple chaotic sequences, two high-sensitivity pseudo-random sequences are generated, and the generated high-sensitivity random sequence is used for synchronization cross-processing in four directions. Using the symmetry of the image, the image is divided into four directions, and the processing of each direction is different based on the high-sensitivity sequence and the chaotic value. Through one traversal, the entire image is processed four times differently. The encryption process is uncontrollable and invisible depending on the chaotic sequence. Simulation test results show that the algorithm has good encryption results, is sensitive to the initial secret key and provides satisfactory security capabilities compared with other algorithms.


